Regulatory change automation converts new rule text into auditable impact actions your teams can assign and track. It detects changes, assesses business impact, routes tasks to the right owners, and logs every step for examination. The outcome is speed, traceability, and controlled human oversight, not unsupervised AI. Governance and explainability stay mandatory at every stage.
TL;DR:
- Start with one jurisdiction or regulatory domain, define detection speed, mapping accuracy, and task completion metrics, then scale only after governance and mapping logic hold.
- Require human approval for legally consequential mapping changes, escalations, and closeout, while retrieval, summaries, and routing can run automatically when immutable logs capture each action.
- Before buying, ask vendors to show a complete audit trail for one change, from detection through approval; inability to produce it rules out the platform.
- Accurate mapping depends more on a canonical, maintained rule repository than on model choice, so assign an owner and review its contents quarterly.
Table of Contents
- What regulatory change automation is and where it fits
- Business benefits backed by industry data
- Core capabilities to evaluate before you buy
- A pilot-to-scale roadmap for legal and compliance teams
- Governance, explainability, and auditability in practice
- Technology considerations: integrations, data, and validation
- Why governed automation is infrastructure, not a tool
- How Neota Logic supports this roadmap
- FAQ
- Sources
What regulatory change automation is and where it fits
Regulatory change automation is the layer that moves a new rule from publication to documented compliance action. It spans four stages: horizon scanning picks up new or amended regulatory text, mapping connects that text to internal obligations, impact analysis translates obligations into affected processes and controls, and task orchestration assigns work with deadlines and ownership.
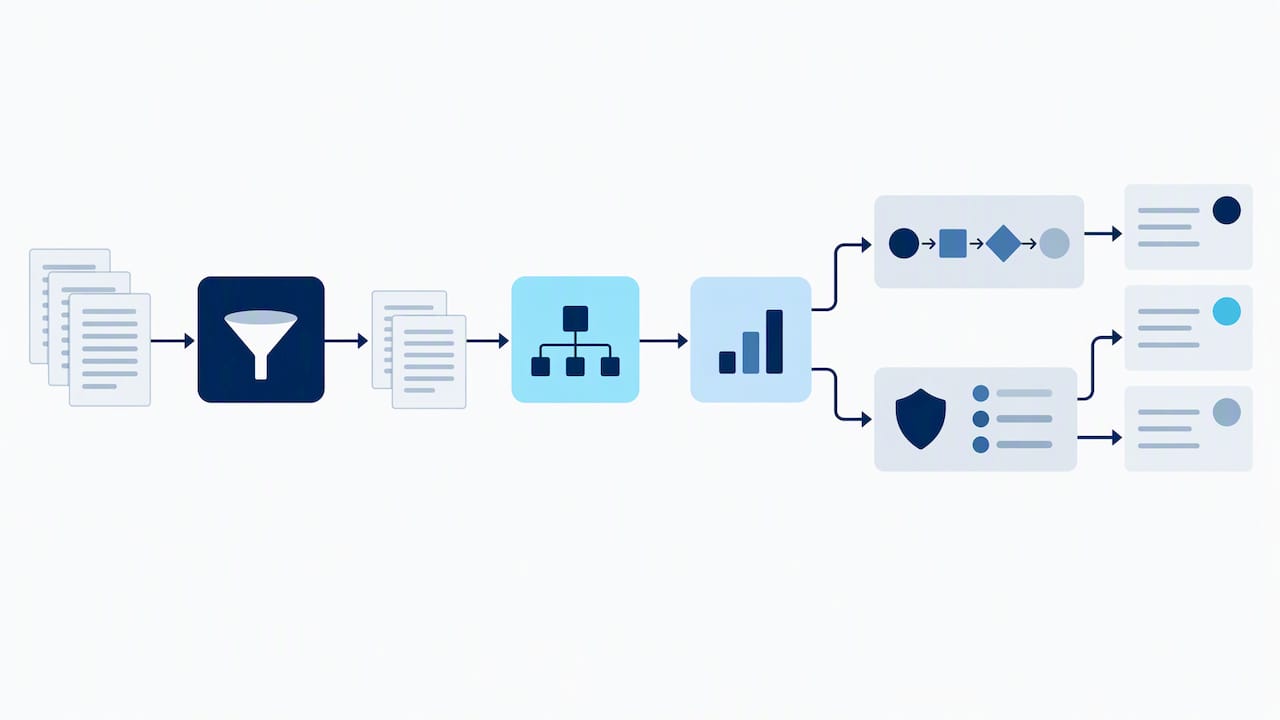
This layer does not replace your policy repository or risk register. It sits between them and the people who act on them, pulling source text, matching it against existing controls, and pushing structured tasks into the systems your teams already use, including ticketing platforms and case management tools.
In practice, this looks like:
- Automated retrieval of new regulatory publications from configured jurisdictions and agencies
- Plain-language summaries of lengthy rule text generated for review, not final interpretation
- Mapping of specific obligations to existing controls, policies, and named owners
- Routing of gaps and exceptions into existing workflow and ticketing systems
The FDIC compliance manual reflects the regulatory expectation behind this structure: documented, traceable processes are a compliance control in their own right, not a byproduct of one.
Business benefits backed by industry data
Faster detection and response are the headline benefits, but the real value shows up in reporting quality and cost discipline. Firms that automate change tracking give first, second, and third line functions a shared, time-stamped record instead of competing spreadsheets.
Rising numbers of firms report increasing their technology and AI investment specifically for compliance activities, with measurable gains in visibility and response speed, according to the Global Compliance Survey 2025 from PwC Switzerland. That same survey finds regulation now reaches into product design, data handling, sustainability reporting, and workforce policy, which means automation has to connect across domains rather than sit inside one compliance silo.
The cost case tends to follow the same pattern across industries:
- Reduced manual research hours spent reading and interpreting new regulatory text
- Fewer missed deadlines because tasks carry owners and due dates automatically
- Lower audit preparation cost when every action already has a timestamp and an owner
- Better internal reporting because leadership sees status in one place, not several
Centralizing compliance activity and consolidating data are explicit recommendations in the PwC global compliance survey, which ties technology investment directly to handling regulatory complexity rather than treating it as a nice-to-have.
Core capabilities to evaluate before you buy
Procurement conversations go faster when you evaluate capabilities, not vendor pitches. Six capability areas separate a real regulatory change automation platform from a notification feed with a dashboard attached.
- Horizon scanning: configurable feeds across the jurisdictions and agencies relevant to your business, not a fixed list
- Change-to-obligation mapping: automatic linkage between new text and existing obligations, with gap analysis when no match exists
- Impact analysis: a structured view of which processes, controls, and business units a change touches
- Workflow orchestration: task assignment, SLA tracking, and escalation built into the platform, not bolted on afterward
- Audit logs and version control: an immutable record of every change, decision, and sign-off
- Explainability controls: a clear accounting of why the system mapped a change the way it did
- Integration surface: APIs and connectors to your document management system, ticketing tool, and policy repository
Ask any vendor to show you the audit log for a single change end to end, from detection through sign-off. If they cannot produce that trail on demand, the platform is not built for a regulated environment.
Pro Tip: Score vendors against the capability list above before you ever watch a demo. Demos sell features; your scoring sheet should test for governance.
A pilot-to-scale roadmap for legal and compliance teams
A pilot works when it is scoped tightly and measured honestly. Scale comes after the pilot proves the mapping logic and the governance model, not before.
- Design the pilot. Pick one jurisdiction or one regulatory domain, define success metrics (detection speed, mapping accuracy, task completion rate), and name the governance owner and stakeholders before any configuration begins.
- Prepare your data. Canonicalize the rule texts you will track, index your existing policies, and build mapping templates that connect obligations to controls in a consistent format.
- Design automation with checkpoints. Build human review into every stage where interpretation is required, and define escalation paths for ambiguous or high-risk changes.
- Run the pilot and measure. Track the metrics you defined, log every exception, and refine mappings based on what the pilot actually surfaces, not what you assumed going in.
- Scale deliberately. Expand jurisdiction coverage, formalize the governance model, train the teams who will own ongoing maintenance, and set continuous improvement metrics tied to audit outcomes.
Stakeholder roles matter more than most pilots budget for. You need a business owner who understands the regulatory domain, a technical owner who understands the integration points, and a governance owner who signs off on how much autonomy the system gets at each stage.
A few practices separate pilots that scale from pilots that stall:
- Keep the pilot’s scope narrow enough that a failure is cheap to diagnose
- Document every mapping decision, including the ones a human overrode
- Review the audit trail weekly during the pilot, not just at the end
- Set a hard date to decide whether to scale, pause, or kill the pilot
Ongoing maintenance of regulatory rules inside the system is not a one-time setup task. Rules change, agencies issue new guidance, and your mapping templates need a scheduled review cycle, typically quarterly, with a named owner responsible for keeping the canonical rule repository current.
Adoption inside legal teams depends on how the system is introduced, not just how it performs. Teams accept automation faster when they see it remove rote research work without removing their judgment calls, and when early wins get communicated back to the people doing the work.
Governance, explainability, and auditability in practice
Governance is the differentiator in regulatory change automation, not the feature list. A platform that automates detection and mapping but cannot explain its own decisions creates a new compliance risk instead of solving one.
Model-agnostic orchestration matters here for a specific reason: it keeps your legal team from being locked into one AI vendor’s interpretation logic. When a model is swapped or updated, your audit trail and your mapping rules stay intact, which protects defensibility during an examination.
Three things belong in every governed deployment:
- An immutable audit log that records what changed, who reviewed it, and when
- Version control on every policy mapping and every automated decision
- Explainability controls that show why the system flagged a change a given way, not just that it did
Audit trails and human checkpoints are not an obstacle to automation speed. They are what makes automation speed defensible in front of a regulator.
Human review belongs at the points where interpretation carries legal consequence: confirming a new mapping between a rule and a control, approving an escalation, and signing off before a change closes out. Everything else, retrieval, summarization, routing, can run without a human in the loop as long as the log shows exactly what happened.
Technology considerations: integrations, data, and validation
Data quality decides whether automation works before any model does. A canonical, well-maintained rule repository is the gating factor for accurate mapping, more than any model choice.
Integration points to confirm before deployment:
- Document management systems, so policy versions and rule texts stay synchronized
- Ticketing and case management tools, so tasks route where your teams already work
- Policy engines and risk registers, so mapping updates propagate automatically
- Reporting systems, so audit trails feed directly into examination-ready output
Model governance should be model-agnostic by design, with human-in-loop checks at defined points and validation testing run against known regulatory changes before go-live. The EY 2023 Global Basel 3 Reforms survey found that data and technology are the top delivery challenges on large regulatory programs, with automation and cloud infrastructure cited as the common response. Enterprise scale introduces its own performance demands: the platform has to keep pace with jurisdiction count and task volume without slowing the review cycle your compliance team depends on.
Why governed automation is infrastructure, not a tool
Regulatory change automation only earns trust when legal and compliance co-own it. Treat it as infrastructure with a named governance model, not as a tool one team installs and others tolerate.
The riskiest deployments we see are bolt-on point tools with no audit trail and no explainability layer attached to the AI doing the mapping. They move fast until an examiner asks why a decision was made, and nobody can answer.
Run your current state against the capability checklist above. The gaps you find there are the gaps that matter.
— Patrick
How Neota Logic supports this roadmap
We provide governed AI infrastructure for legal and compliance teams. Our workflows include audit trails, version control, and explainability controls by default, emphasizing governance as the key to automation defensibility.
Our platform maps directly onto the roadmap above:
- We classify and route regulatory and legal requests through configurable no-code workflows.
- We orchestrate multiple AI models without vendor lock-in.
- We log every action for audit to support examination readiness from the start.
- We integrate with document management, ticketing, and policy systems your teams use.
If the gaps you found against the capability checklist point toward governed infrastructure rather than another point tool, see how our solutions map to your roadmap, or go straight to pricing and plan details to start the conversation.
FAQ
What is automated compliance software?
Automated compliance software monitors regulatory sources, maps changes to internal obligations, and routes resulting tasks to the people responsible for acting on them. It typically includes audit logging and reporting so every action can be reviewed later.
What is regulatory change management?
Regulatory change management is the structured process of identifying new or amended regulations, assessing their impact on your business, and updating policies, controls, and procedures accordingly. Automation supports this process but does not replace the governance decisions behind it.
What is regulatory reporting?
Regulatory reporting is the formal submission of data and documentation to a regulator or supervisory body, demonstrating compliance with applicable rules. Automated systems support this by generating audit trails and status records that feed directly into reporting workflows.
What is the regulatory process?
The regulatory process covers how a rule or regulation is proposed, finalized, published, and then adopted and enforced within regulated industries. For compliance teams, the relevant stage begins the moment a rule is published and must be assessed for business impact.
How long does it take to implement regulatory change automation?
Timelines vary by scope, but a narrowly defined pilot covering one jurisdiction or domain is the common starting point before any broader rollout. Scaling depends on how quickly the pilot’s mapping accuracy and governance model prove out.
Sources
Ready to make your AI workflows defensible?
Book a demo and we'll walk one of your real processes through Neota.
Book demo