Legal workflow orchestration sequences people, systems, and governed AI into auditable end-to-end legal processes that cut cycle time while preserving human oversight. It is not a faster way to run one task. It is a controlled pipeline from intake to obligation tracking. Governance and audit trails are what make it defensible when a regulator, a court, or your board asks how a decision was made.
TL;DR:
- Choose a high volume, moderate risk pilot, define its baseline first, and install audit logs, a model inventory, and test harnesses before live traffic.
- For AI steps, record each model’s version, owner, inputs, prompts, and outputs, then require lawyer approval whenever an output creates legal consequences.
- Name one canonical source for matter and document state, route updates through defined APIs or middleware, and preserve immutable event logs as audit evidence.
- CLOC reports that 66% of legal departments rank automation as a high priority, but pilot results still require baseline measurements.
Table of Contents
- What is the difference between orchestration and automation?
- What are the core components of an orchestration stack?
- How do you embed governed AI so it holds up under scrutiny?
- How do you stitch fragmented systems into one source of truth?
- What should a deployment checklist look like?
- Which metrics prove that orchestration is working?
- Why governance has to come first
- Neota Logic: governed workflow orchestration for legal teams
- FAQ
- Sources
What is the difference between orchestration and automation?
Point automation speeds up one task. Orchestration sequences tasks, systems, people, and AI into a single pipeline, and it carries policy, handoffs, and state from step to step. When a contract moves from intake to review, orchestration knows who owns it, which rule applied, and what happens if an approver stalls.
That distinction matters because most legal teams already own a pile of point tools. The gap is the connective tissue between them. Industry data frame this as an orchestration era where the main challenge is stitching fragmented systems and teams together into policy-compliant, end-to-end processes.
Orchestrated flows show the pattern:
- Contract path: intake, triage, review routing, approval, e-signature, then obligation tracking.
- Legal request path: classification, matter assignment, SLA timer, and escalation to the right attorney.
- Compliance path: a policy question is answered by approved logic, and exceptions go to a human reviewer with the full record attached.
What are the core components of an orchestration stack?
You need core building blocks. Skip one and the pipeline leaks.
- Intake and classification: every request enters through one door and is typed, scored, and tagged on arrival.
- Decision logic and routing: deterministic rules assign work and enforce SLAs.
- Human checkpoints: named roles own named handoffs, so no step is anonymous.
- Document generation and versioning: templates, tracked versions, and e-signature tie into the record.
- Audit trails and integrations: immutable logs, plus connections to your document management system and matter systems.
Document management is not a separate project. It is a component. If versions live outside the pipeline, the audit trail has a hole in it.
Pro Tip: Write the audit requirement for each step before you build the step. If you cannot say what evidence the step must leave behind, the step is not ready.
How do you embed governed AI so it holds up under scrutiny?
Use AI where it earns its place: classification, summarization, and decision support inside the pipeline. Do not let it act outside the pipeline. The orchestration layer is what turns a model output into a governed, attributable event.
Anchor your controls to the NIST AI Risk Management Framework. Its four functions, GOVERN, MAP, MEASURE, and MANAGE, are meant to run across the AI lifecycle, supported by policies, accountability structures, documentation, and periodic review. The generative AI profile adds suggested actions on transparency, provenance, and incident response.
Practitioners reach the same conclusion from the operations side:
Capability without control is a liability, and governance is cross-system, not a siloed policy. Gen AI and the Practice of Law 3 report, as summarized by Legal IT Insider
Ungoverned generative AI creates forensic exposure. You cannot defend an output you cannot trace. Embed these controls:
- Model inventory: know every model in use, its version, and its owner.
- Provenance logging: record inputs, prompts, outputs, and the model version for each call.
- Human-in-the-loop gates: a lawyer approves anything that creates legal consequence.
- Versioning and test harnesses: change a model or prompt only after it passes your tests.
- Incident plan: define who acts, and how, when a model misbehaves.
How do you stitch fragmented systems into one source of truth?
Start with an inventory of every system that touches a matter: email, intake forms, the DMS, the matter system, the e-signature tool, the CRM. Map where each fact originates and where it is copied. Legal teams may discover conflicting versions of the same status.
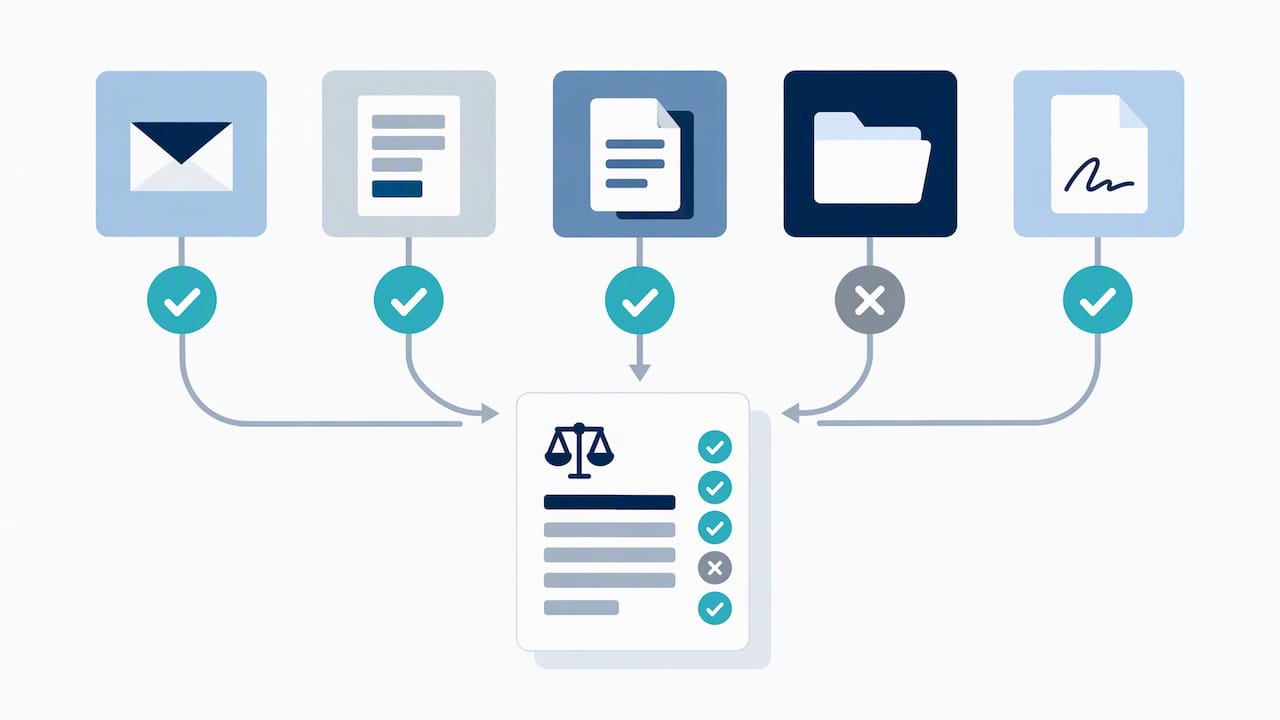
Then name one canonical source for matter and document state. Everything else reads from it or writes to it through a defined path. Data architecture is the unglamorous precondition for everything else, a point the Gen AI and the Practice of Law 3 report makes directly.
Design choices that hold up:
- Event-driven updates: each state change is an event, not an overwrite.
- Idempotent writes: replaying an event never corrupts the record.
- Immutable event logs: the log becomes your audit evidence.
- Middleware or APIs over point-to-point links: fragile direct connections break silently.
Logging pattern matters here. Metadata-based logging can produce audit-ready evidence without copying sensitive content into yet another system, which also eases the security and privacy burden on your orchestration layer.
What should a deployment checklist look like?
Follow the order. Governance goes in before production, not after.
- Discover: map current processes, owners, and pain points.
- Prioritize: rank candidate flows by volume, risk, and return.
- Define: write decision logic, SLAs, and human checkpoints up front.
- Build controls first: stand up audit logs, the model inventory, and test harnesses before any live traffic.
- Pilot: run one flow with real users and a real baseline.
- Measure and revise: compare against the baseline and fix what the data exposes.
- Scale: add flows, train teams, and manage the change deliberately.
Set realistic expectations. A governed pilot takes time, and adoption follows trust. Lawyers adopt what they can inspect. Change management is not a closing step. Name champions in each practice area early, and show them the audit trail before you show them the speed gains.
Scale needs no rebuild if you design for it. Teams of different sizes can run the same pipeline pattern with different rules, volumes, and role assignments.
Pro Tip: Pick a pilot flow with high volume and moderate risk. Low-volume flows prove nothing. High-risk flows stall in review before you learn anything.
Which metrics prove that orchestration is working?
Measure before you build. Without a baseline, every improvement claim is an opinion.
- Cycle time and time to resolution: from request to closed.
- Lawyer touch time: minutes a lawyer spends per matter.
- Error rate: rework, wrong routing, and missed clauses.
- SLA compliance: share of requests handled inside the target.
- Adoption: how many requests actually enter through the orchestrated path.
Pull the numbers from your orchestration event logs and DMS or matter metadata. Do not rely on self-reported time. The demand is there: 66% of legal departments identify automation as a high priority, according to the CLOC State of the Industry report. Priority is not proof. Your own baseline is.
Why governance has to come first
Here is my position. Most legal teams will buy capability before they buy control, and most will regret the order. A fast pipeline that cannot explain itself is a liability with a good interface.
Start small. Prove control on one flow. Show your auditors the log. Then scale. Auditability and human oversight are not the price of orchestration. They are the product.
— Patrick
Neota Logic: governed workflow orchestration for legal teams
Neota Logic is governed AI infrastructure for legal and compliance teams. We are not a point solution and we are not a chatbot. Governance is what we build, and audit trails, versioning, and explainability are how you defend what the pipeline does.
Our platform gives you:
- Workflow and document automation designed for your team to manage.
- Multi-model AI integration.
- Audit trails and human oversight support governed steps.
- Use cases include intake and triage, contract automation, compliance advisory, and obligation tracking.
See how this maps to your own flows. Review our solutions, then book a demo or start a discovery sprint with our team.
FAQ
What is legal workflow orchestration in simple terms?
It is the coordinated sequencing of people, systems, and governed AI across a legal process, from intake to completion. Unlike single-task automation, it carries policy, handoffs, and audit evidence through every step.
How is orchestration different from legal process automation?
Automation speeds up one task. Orchestration connects many tasks into one controlled pipeline with defined owners, rules, and records. You can automate without orchestrating, but you cannot govern at scale without it.
Which framework should guide AI governance in legal workflows?
The NIST AI RMF is a practical anchor. Its four functions, GOVERN, MAP, MEASURE, and MANAGE, map cleanly onto model inventories, provenance logging, and human review gates.
What should we measure first?
Capture a baseline for cycle time, lawyer touch time, and SLA compliance before you launch. Orchestration event logs then show whether the pilot moved those numbers.
Sources
- Based on the 2024 Harbor Law Department Survey in Collaboration with CLOC
- Tonkean Releases Survey of 300 Legal Ops Executives: “The State of the Legal Operations Tech Stack”
- Artificial Intelligence Risk Management Framework (AI RMF 1.0)
- Gen AI and the Practice of Law 3 Report: Governance is the Key, not the Lock - Legal IT Insider
Ready to make your AI workflows defensible?
Book a demo and we'll walk one of your real processes through Neota.
Book demo